PROJECT FILE / CASE STUDY

Splunk Firewall Monitoring

Turning firewall logs into dashboards and queries for initial investigation.

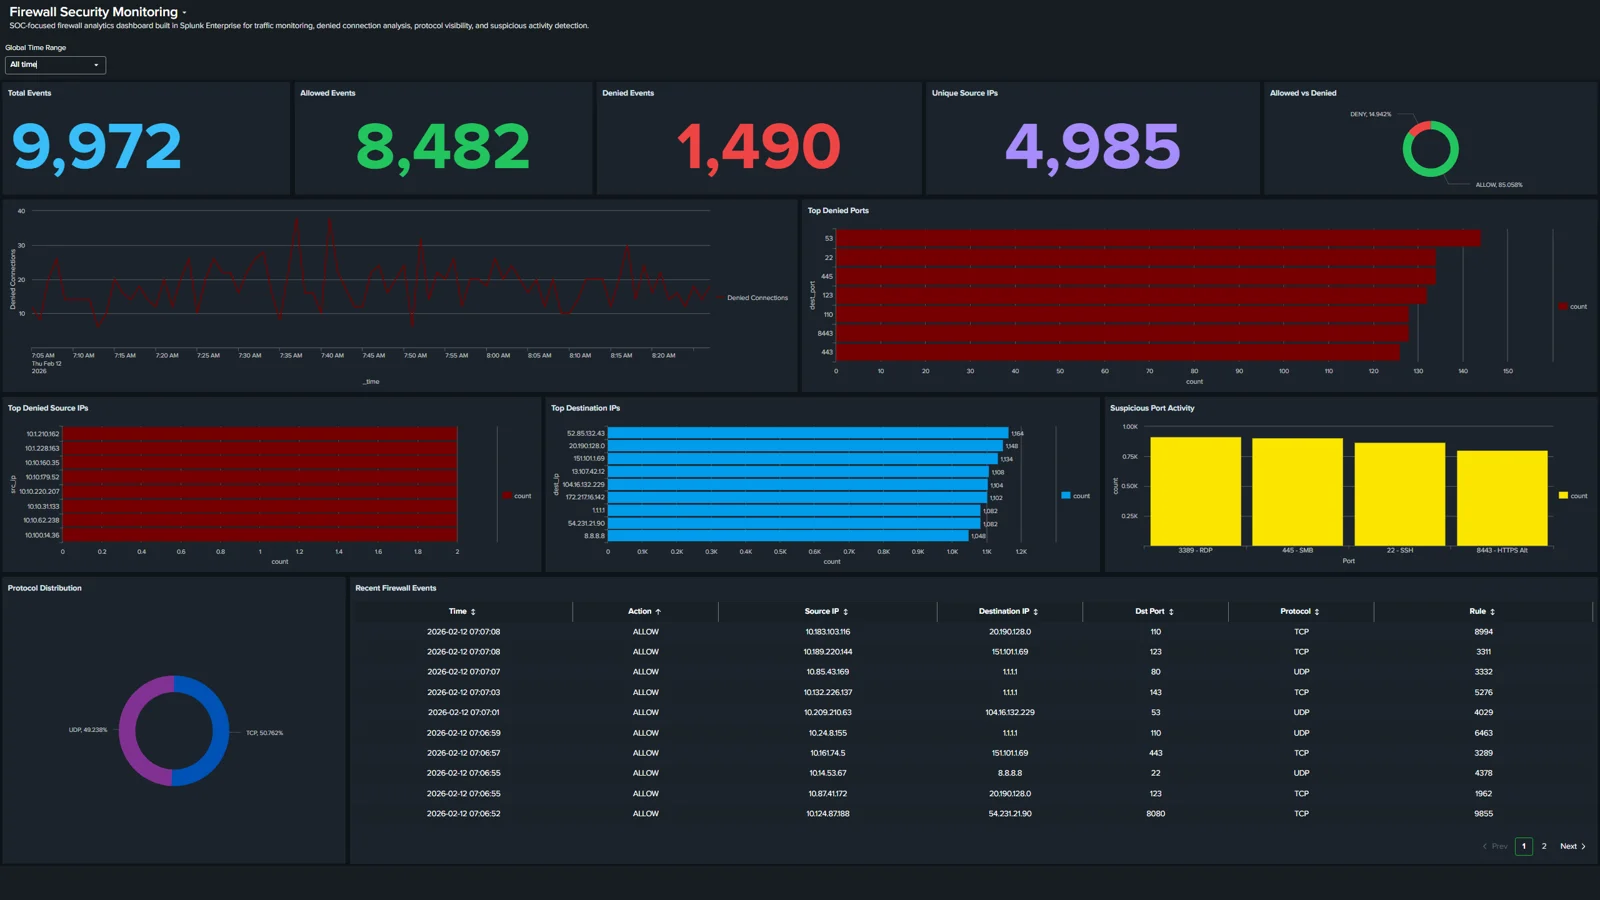
Original screenshot of Splunk Firewall Monitoring
SP / PROJECT FILE
Original interface
DisciplineCybersecurity
Evidence statusDocumented in the README; not independently operationally verified.
AttributionA collaborative project by Meshal Jathmi and Maysam, according to the README.
01 / CONTEXT

Challenge & context

Making raw events useful for analyst review.

02 / APPROACH

Solution approach

SPL queries, regex fields and port/destination dashboards provide triage signals, not independent proof of an attack.

03 / DOCUMENTED CAPABILITIES

What the available evidence supports

  • Structured log field extraction
  • Allowed and denied connection views
Back to all projects
KEEP EXPLORING

In the same orbit.